
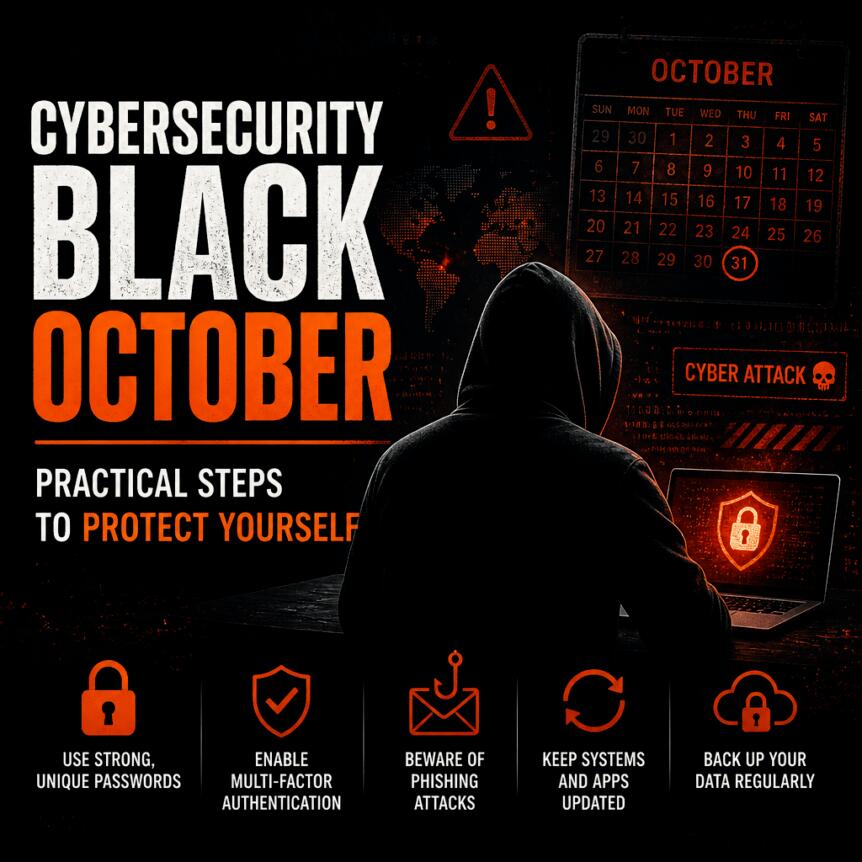
“Black October” is already turning into one of the most disruptive stretches the internet has seen in recent months, with security researchers and operators pointing to fast-moving vulnerabilities, automated scanning, and repeated incidents across widely used software and services. The situation escalated after critical flaws in PHP—an open-source programming language used by a large share of websites—were publicly disclosed, prompting an immediate scramble to patch and harden systems.
Reporting from across the security industry describes how the window between disclosure and exploitation is shrinking. Cloudflare said it observed millions of attempts to exploit the newly disclosed PHP vulnerability after the disclosure, following thousands of attempts in the hours prior. Meanwhile, some governments and security agencies urged urgent action, including patching immediately or taking affected systems offline.
Key takeaways
- PHP vulnerabilities disclosed by the PHP Foundation triggered rapid exploitation attempts, with Cloudflare reporting millions of attempts after publication.
- Multiple public-facing disruptions and breaches—from cloud credential exposure to certificate weaknesses—underline how shared infrastructure can amplify impact.
- Security leaders warn that AI is speeding up vulnerability discovery, but not necessarily accelerating the capacity to fix, test, and deploy patches at scale.
- For individuals, the most actionable steps center on MFA, reducing account and device exposure, and avoiding risky logins during the highest-risk window.
- Crypto users can reduce personal risk through better custody hygiene, but experts stress that the structural burden still lies with platforms and providers.
PHP patch scramble shows how quickly attackers move
According to the PHP Foundation, critical PHP security issues were released with guidance on strengthening PHP security, and the subsequent operational response began almost immediately. Cloudflare reported millions of attempts to exploit the vulnerability after disclosure, noting thousands of attempts in the preceding hours. That pattern is consistent with attackers treating public security advisories as a launchpad for automated scanning and exploitation.
The urgency extended beyond purely technical channels. Some countries, including France and Finland, temporarily restricted access to certain websites while organizations worked to mitigate the risk. In the United States, the NSA warned organizations to patch the flaws quickly or take affected systems offline, signaling that the vulnerability was considered serious enough to warrant government-level guidance.
Shared infrastructure failures are multiplying the blast radius
Beyond the PHP incident, multiple separate security events described during the same window are reinforcing a broader theme: weaknesses in shared infrastructure can expose many organizations at once. A bitcoin security researcher involved with Bitcoin Red Team, Rob Hamilton, told Magazine that the current situation appears to mirror the state of risk the broader internet already recognized “three months ago,” suggesting that the threat environment is not only recurring—it is becoming more widely acknowledged.
Other examples highlighted in the coverage include disclosures and incidents involving credentials, patient data, certificate authorities, and developer infrastructure:
- Cloud platform Railway disclosed an incident in which an attacker accessed and decrypted customer credentials and API keys, apparently targeting AI providers.
- Quest Diagnostics confirmed a breach involving private patient health data.
- Indian security firm eMudhra reported findings related to certificate authorities with weak keys that could enable impersonation of trusted websites.
- GitHub experienced a major service disruption, underscoring how dependent much of software development is on centralized platforms.
GitHub senior director of security Austin Devers emphasized that “reliability requires constant work,” because modern development environments are “so connected.” Jonathan Riss, an OSINT and blockchain intelligence analyst at CertiK, also warned that a single weakness in shared infrastructure can simultaneously expose many organizations—an asymmetry that defenders can struggle to mitigate quickly.
Riss added a second, more operational concern: even if AI helps identify vulnerabilities faster, it does not automatically increase the ability to remediate them at the same speed. “Finding vulnerabilities faster does not automatically give us the capacity to resolve them faster,” he said.
AI is shifting cybersecurity economics—and defender capacity
A recurring argument across security commentary is that AI has changed the economics and accessibility of cyberattacks. Where some intrusions once required significant resources, attackers can now scale reconnaissance and vulnerability hunting with tools that lower technical barriers. One implication is that the time between a vulnerability becoming public and it being actively exploited is getting shorter.
Matt Shumer, an AI entrepreneur and investor, argued that AI can help non-technical users identify weak spots and exploit them, while defenders are left “racing to keep up.” Devers similarly described AI-assisted security tooling as “dramatically” lowering barriers for uncovering “complex, deep-seated flaws” in widely used codebases.
But the remediation challenge remains the bottleneck. Even when a vulnerability is well understood, patching is not a single action—it requires testing, deployment, and ongoing maintenance across enormous numbers of systems. That is why some risk-management strategies focus less on “preventing” compromise entirely and more on limiting how far an intrusion can spread once it starts.
Practical steps for individuals: reduce exposure, tighten access
While infrastructure-level problems are difficult for individuals to solve, the coverage outlines several concrete measures that can reduce personal risk during periods of aggressive exploitation.
Matt Shumer recommended avoiding unfamiliar sites and refraining from entering passwords or card details on unknown domains “until this blows over.” He also pointed to the reality that smaller sites are often slower to patch, which can make them disproportionately risky during the early phase of an outbreak.
Devers focused on access control and footprint reduction. He recommended turning on Multi-Factor Authentication (MFA) across accounts, ideally using an authenticator app or a hardware security key rather than SMS. The goal is to create a “circuit breaker” that prevents unauthorized logins even if underlying credentials or parts of software are compromised.
Other widely reinforced steps include:
- Using unique, strong passwords for every account and avoiding password reuse.
- Periodically disconnecting old permissions and third-party integrations that are no longer needed.
- Keeping devices and web browsers updated, with automatic updates where possible, so attackers can’t exploit personal devices as a pathway into accounts.
- Staying away from risky logins on unfamiliar sites and deleting apps that aren’t used.
Importantly, security experts also stressed what these steps cannot do. Riss described personal actions as ways to “reduce blast radius,” not prevent infrastructure compromise. In other words, good cyber hygiene helps, but it does not eliminate systemic risk driven by platform and provider security.
Crypto custody: better hygiene, but shared risk remains
With incidents mounting, some crypto holders have looked for alternatives to mainstream hardware wallet guidance, while others have cautioned against overreacting by abandoning self-custody altogether. Bitcoin advocate and Casa chief security officer Jameson Lopp reiterated that giving up control of private keys does not eliminate risk—it relocates it to a party you do not control.
The practical takeaway from the crypto-focused security commentary is not to treat self-custody as a magical shield, but to organize holdings and signing behavior to reduce exposure. Riss recommended separating smaller amounts intended for active use into a hot wallet while keeping longer-term funds in a hardware wallet, and he urged users to read signing prompts carefully rather than approving blindly.
As with broader cybersecurity, individual precautions can lower personal vulnerability, but they cannot change how quickly providers patch or how resilient shared infrastructure is to exploitation.
Going forward, the key thing readers should watch is whether patching and deployment keep pace with exploitation attempts—especially for widely used components like PHP and other shared services. As security leaders note, the gap between “finding vulnerabilities” and “fixing and installing them everywhere” may define how long Black October stays dangerous.
https://www.cryptobreaking.com/cybersecurity-black-october-practical-steps/?utm_source=blogger%20&utm_medium=social_auto&utm_campaign=Cybersecurity%20Black%20October:%20Practical%20steps%20to%20protect%20yourself%20
Comments
Post a Comment